ManageEngine Unified endpoint management and security solutions
Contact us for pricing
Product Details
Key Features
Unified Multi-OS Endpoint Management: Manage Windows, macOS, Linux, iOS, iPadOS, Android, and IoT devices from a single console using the Management Plane and Communication Layer.
Zero‑Touch and Bulk Enrollment: Deploy devices instantly with Apple ABM/ASM, Android Zero‑Touch, Windows Autopilot, or bulk QR/CSV/API enrollment.
Comprehensive EDR and Threat Detection: Behavioral analytics, MITRE ATT&CK‑mapped rules, and process tree visualization protect endpoints in real time.
Automated Patch and Vulnerability Management: OS and third‑party patches roll out via staged rings while CVE scanning prioritizes fixes by CVSS scores.
Granular Identity & Access Controls: Conditional Access, certificate‑based auth, SSO (SAML/OIDC) and step‑up MFA enforce zero‑trust policies.
Built‑in Data Protection: FileVault and BitLocker encryption with key escrow, plus DLP controls for USB, clipboard, and screenshots.
Compliance Automation: Pre‑built NIST, ISO, HIPAA, PCI‑DSS, GDPR templates feed real‑time dashboards and auto‑remediation workflows.
Scalable Architecture: Supports 250,000+ endpoints per tenant, multi‑region HA, and region‑pinned data residency for GDPR compliance.
Extensive Integration Ecosystem: Native connectors to SIEMs, SOARs, IdPs, ITSM tools, and STIX/TAXII threat feeds streamline operations.
Platform Self‑Hardening: SOC 2 Type II/ISO 27001 certification, RBAC, immutable audit trails, HSM‑backed secrets vault, and quarterly penetration testing.
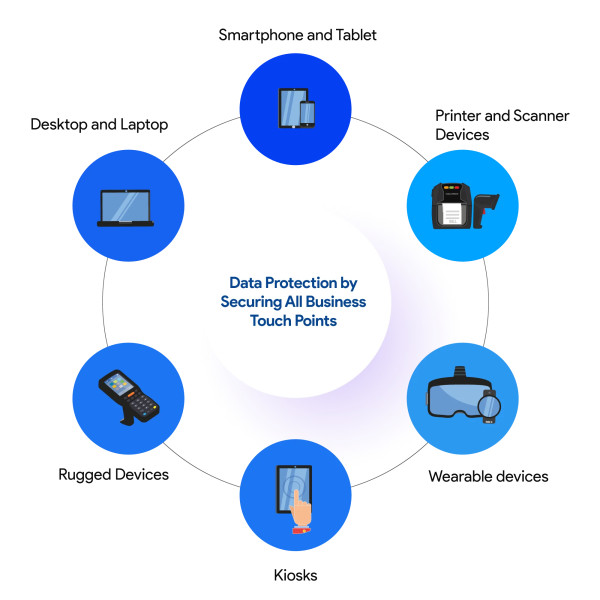
Product Overview | A centralized platform that discovers, provisions, monitors, secures, and manages every endpoint in an organization — desktops, laptops, smartphones, tablets, servers, IoT, and rugged/kiosk devices — across Windows, macOS, Linux, iOS, iPadOS, and Android, from a single cloud or on-prem console. |
Management Plane | Cloud-hosted (multi-tenant SaaS) or on-prem console; REST API-first design |
Communication Layer | Agent-based + agentless (native MDM APIs: Apple DEP/ABM, Android Enterprise, Windows MDM/Intune-style CSPs) |
Data Layer | Encrypted device inventory DB, policy engine, telemetry pipeline (typically Kafka/event-stream backed) |
Enforcement Layer | Policy push via OS-native management channels (APNs for Apple, FCM for Android, WNS/native MDM for Windows) |
Integration Layer | SIEM/SOAR connectors, IAM/SSO (SAML/OIDC), ITSM (ServiceNow/Jira), ticketing webhooks |
Device Management – Zero-touch enrollment | Apple ABM/ASM, Android Zero-Touch, Windows Autopilot |
Device Management – Bulk enrollment | via QR/CSV/API |
Device Management – OS-level configuration profiles | Wi-Fi, VPN, certificates, email |
Device Management – Remote wipe / selective wipe | corporate data only vs. full device |
Device Management – Geofencing and location tracking | opt-in, privacy-compliant |
Device Management – Kiosk/single-app mode | for rugged and shared devices |
Endpoint Security – EDR | behavioral analytics, MITRE ATT&CK-mapped detection rules, process tree visualization |
Endpoint Security – Patch Management | automated OS + third-party app patching with staged rollout rings (canary → pilot → broad) |
Endpoint Security – Vulnerability Management | CVE scanning against NVD feed, CVSS-based prioritization |
Endpoint Security – Endpoint Encryption | FileVault (macOS), BitLocker (Windows) key escrow and recovery |
Endpoint Security – Application Control | allowlisting/denylisting, sandboxing untrusted binaries |
Endpoint Security – DLP | USB/peripheral control, clipboard restriction, screenshot blocking on managed apps |
Identity & Access – Conditional Access policy engine | device compliance + user risk + network context |
Identity & Access – Certificate-based authentication | SCEP/PKI integration |
Identity & Access – Single Sign-On | SAML 2.0 / OIDC with major IdPs (Okta, Entra ID, Ping) |
Identity & Access – Risk-based adaptive access | step-up MFA on anomaly detection |
Compliance & Reporting – Pre-built templates | NIST 800-53, CMMC 2.0, ISO 27001, HIPAA, PCI-DSS, GDPR |
Compliance & Reporting – Real-time compliance dashboards | with drift detection |
Compliance & Reporting – Automated remediation workflows | non-compliant device → auto-quarantine → VLAN isolation |
Compliance & Reporting – Audit-ready exportable logs | SIEM-forwarded, immutable retention |
Supported OS | Windows 10/11, macOS 12+, iOS/iPadOS 15+, Android 10+, select Linux distros (Ubuntu, RHEL) |
Deployment Models | SaaS (multi-tenant), Private Cloud, On-Prem, Hybrid |
API | REST/JSON, OAuth 2.0 auth, rate-limited (configurable), Webhooks for event push |
Encryption | AES-256 at rest, TLS 1.2+/1.3 in transit |
Agent Footprint | <50MB installed, <2% CPU idle overhead (typical benchmark range) |
Scalability | Tested to 250,000+ managed endpoints per tenant (architecture-dependent) |
High Availability | Multi-region failover, 99.9% SLA (SaaS tier) |
Data Residency | Region-pinned tenancy options (US/EU/APAC) for GDPR/data-sovereignty compliance |
Offline Enforcement | Local policy cache for disconnected/air-gapped endpoint enforcement |
Integration Ecosystem – SIEM | Splunk, Microsoft Sentinel, QRadar, Elastic |
Integration Ecosystem – SOAR | Palo Alto XSOAR, Splunk SOAR |
Integration Ecosystem – IAM/IdP | Entra ID, Okta, Ping Identity |
Integration Ecosystem – ITSM | ServiceNow, Jira Service Management |
Integration Ecosystem – Threat Intel Feeds | STIX/TAXII compatible ingestion |
Security Controls – Certifications | SOC 2 Type II / ISO 27001 certified infrastructure |
Security Controls – RBAC | Role-Based Access Control (RBAC) with granular admin scoping |
Security Controls – Audit trail | Full audit trail of all console actions (who/what/when, immutable) |
Security Controls – Secrets management | via HSM-backed key vault |
Security Controls – Penetration testing | Regular third-party penetration testing (quarterly) |
Licensing Tier – Essentials | MDM, basic patching, compliance reporting |
Licensing Tier – Professional+ | EDR, conditional access, DLP |
Licensing Tier – Enterprise+ | Zero Trust engine, SOAR integration, dedicated tenancy, custom SLA |
Description
Unified endpoint management and security solutions
Key Features & Benefits:
- Unified Multi-OS Endpoint Management: Manage Windows, macOS, Linux, iOS, iPadOS, Android, and IoT devices from a single console using the Management Plane and Communication Layer.
- Zero‑Touch and Bulk Enrollment: Deploy devices instantly with Apple ABM/ASM, Android Zero‑Touch, Windows Autopilot, or bulk QR/CSV/API enrollment.
- Comprehensive EDR and Threat Detection: Behavioral analytics, MITRE ATT&CK‑mapped rules, and process tree visualization protect endpoints in real time.
- Automated Patch and Vulnerability Management: OS and third‑party patches roll out via staged rings while CVE scanning prioritizes fixes by CVSS scores.
- Granular Identity & Access Controls: Conditional Access, certificate‑based auth, SSO (SAML/OIDC) and step‑up MFA enforce zero‑trust policies.
- Built‑in Data Protection: FileVault and BitLocker encryption with key escrow, plus DLP controls for USB, clipboard, and screenshots.
- Compliance Automation: Pre‑built NIST, ISO, HIPAA, PCI‑DSS, GDPR templates feed real‑time dashboards and auto‑remediation workflows.
- Scalable Architecture: Supports 250,000+ endpoints per tenant, multi‑region HA, and region‑pinned data residency for GDPR compliance.
- Extensive Integration Ecosystem: Native connectors to SIEMs, SOARs, IdPs, ITSM tools, and STIX/TAXII threat feeds streamline operations.
- Platform Self‑Hardening: SOC 2 Type II/ISO 27001 certification, RBAC, immutable audit trails, HSM‑backed secrets vault, and quarterly penetration testing.
Ideal For:
- Large enterprises seeking unified endpoint management across diverse OS environments
- Managed service providers needing multi‑tenant SaaS or private cloud deployment
- Compliance‑focused organizations in regulated sectors such as finance, healthcare, and government
- IT security teams requiring integrated EDR, DLP, and zero‑trust capabilities
- Remote workforces that need secure, zero‑touch device provisioning and management
- Educational institutions managing thousands of student and staff devices
- Manufacturing and field operations with rugged/kiosk devices and offline enforcement needs
Summary:
Revolution Technology BD offers a cloud or on‑prem unified endpoint management and security platform that supports Windows, macOS, Linux, iOS, iPadOS, Android, and IoT devices. Key specs include zero‑touch enrollment, integrated EDR, automated patching, conditional access, and compliance templates, all scalable to over 250,000 endpoints with multi‑region high availability. The solution is ideal for enterprises, MSPs, and regulated organizations seeking a single console for device lifecycle, security, and governance. Available through SaaS, private cloud, on‑prem, or hybrid models with flexible licensing tiers.
How to Order
Revolution Technology BD has made shopping easier for customers. Follow these steps:
- Click Register Button from home page
- Register with: Name + Email + Mobile + Password
- Click Create Account after entering information
- Login automatically or use Login button
- Provide mobile number and password, then Sign Up
- Choose desired product and click Buy Now
- View product details and click Add to Cart
- Click Item box (upper right corner)
- Go to Shopping Cart page
- Continue Shopping for more products or proceed
- Click "Click Here to Address" button
- Provide Full Name, Phone, Email & Delivery Address
- Click Order Submit button
- View Bill Invoice and receive email confirmation
- Print Invoice using Print button
- Wait for delivery - we'll keep you updated
- Thank you for shopping with us!